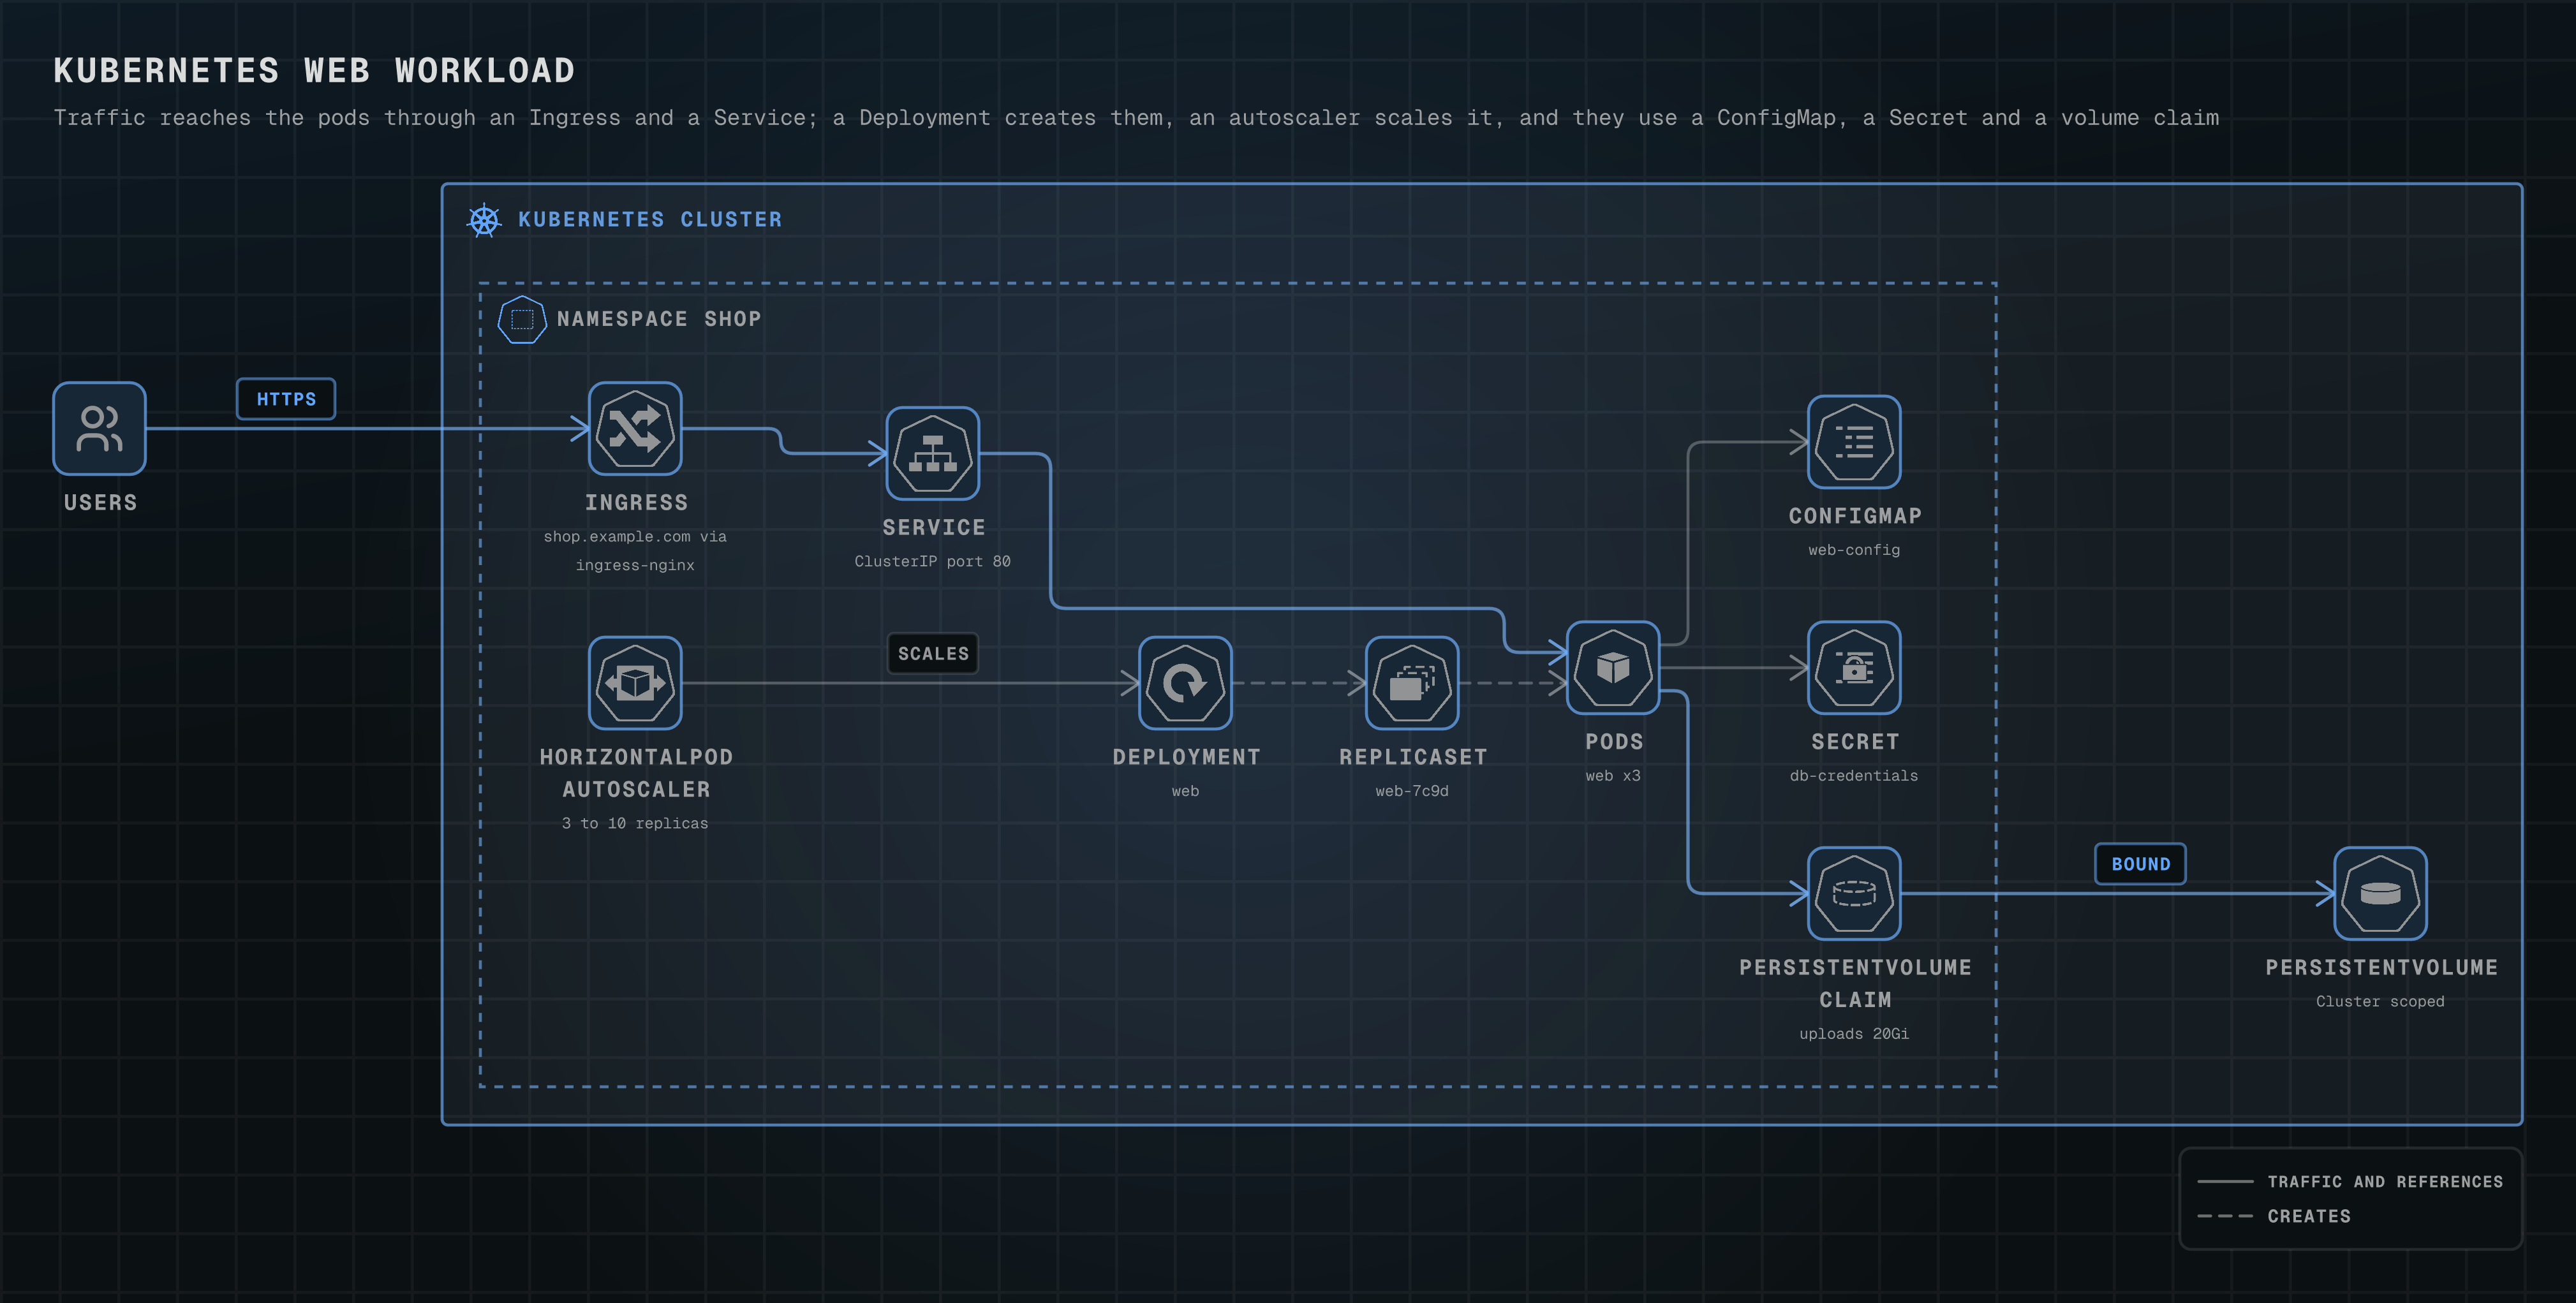
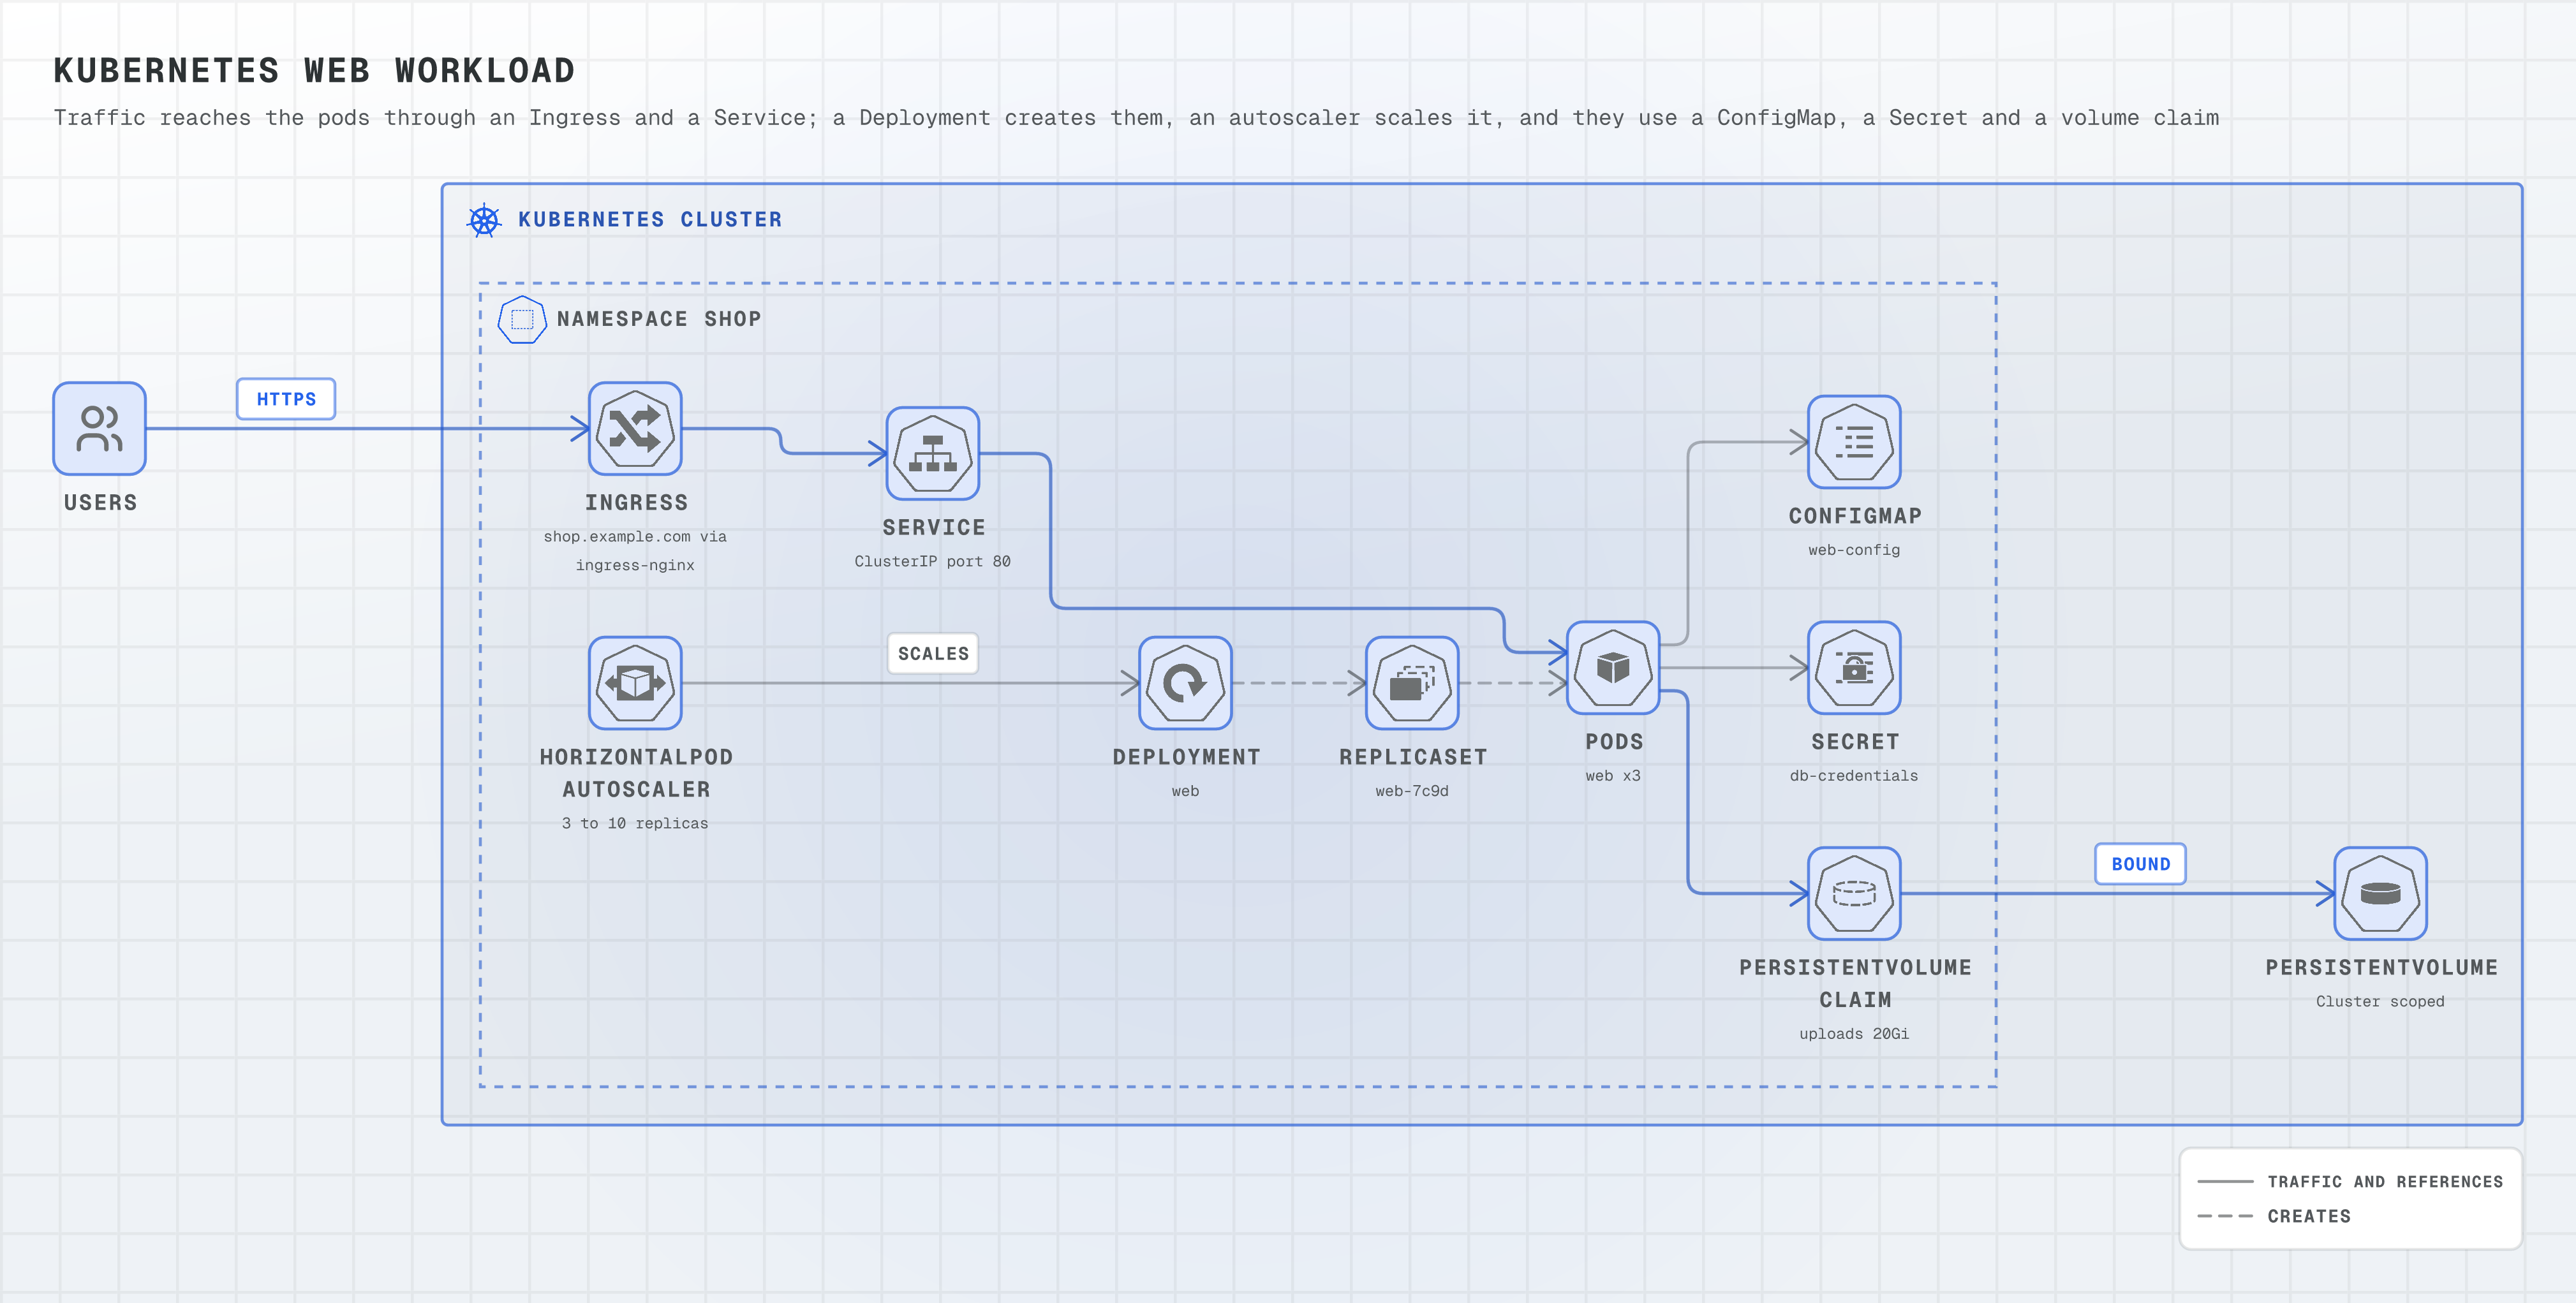
Kubernetes web workload
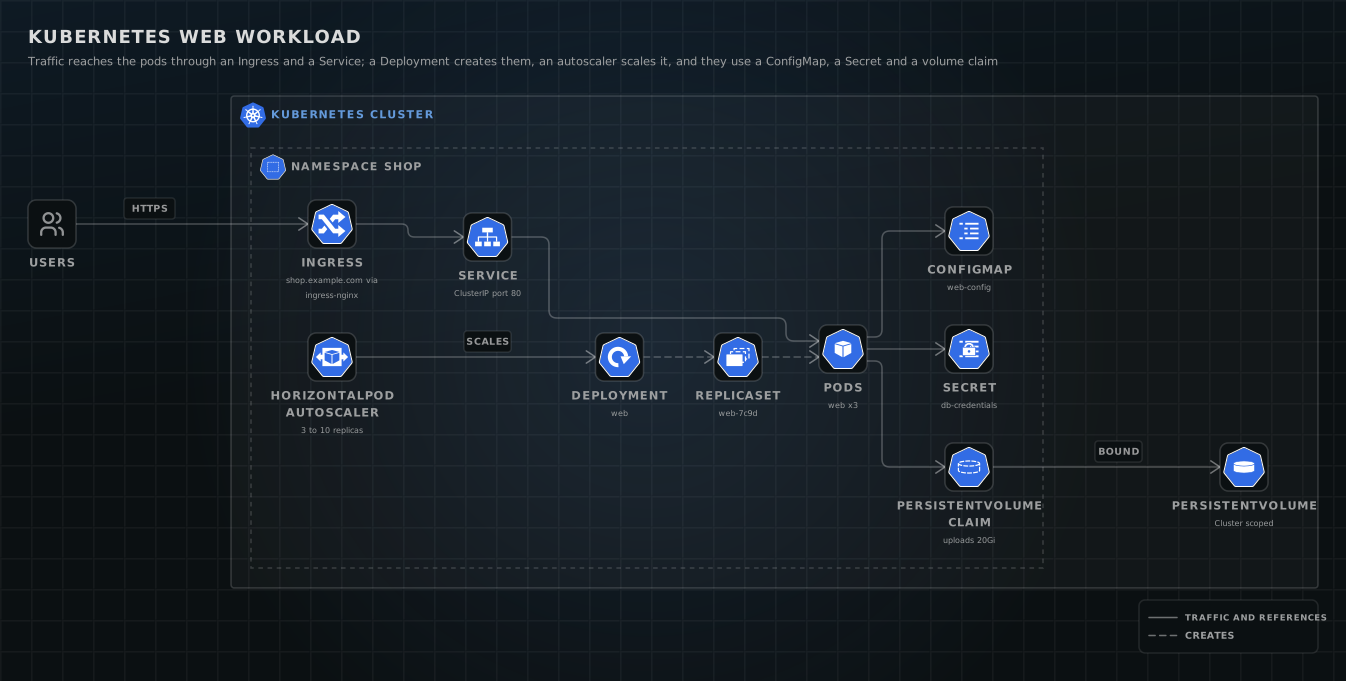
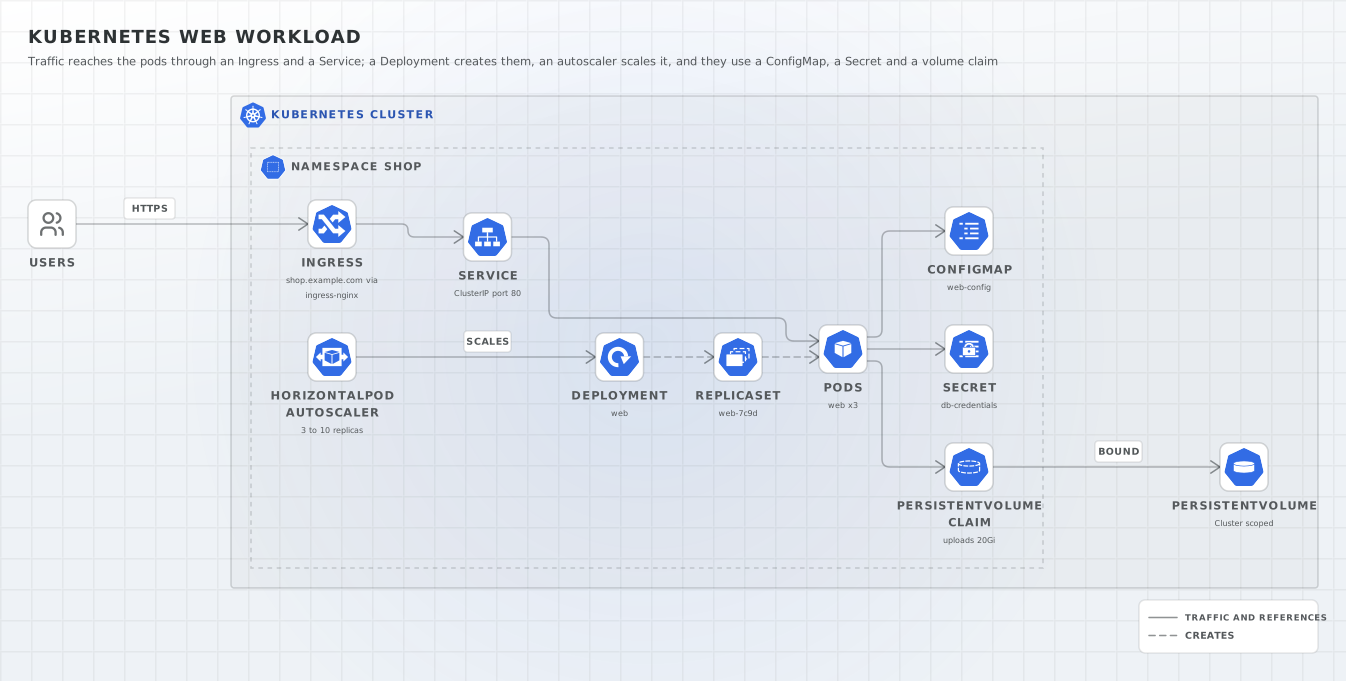
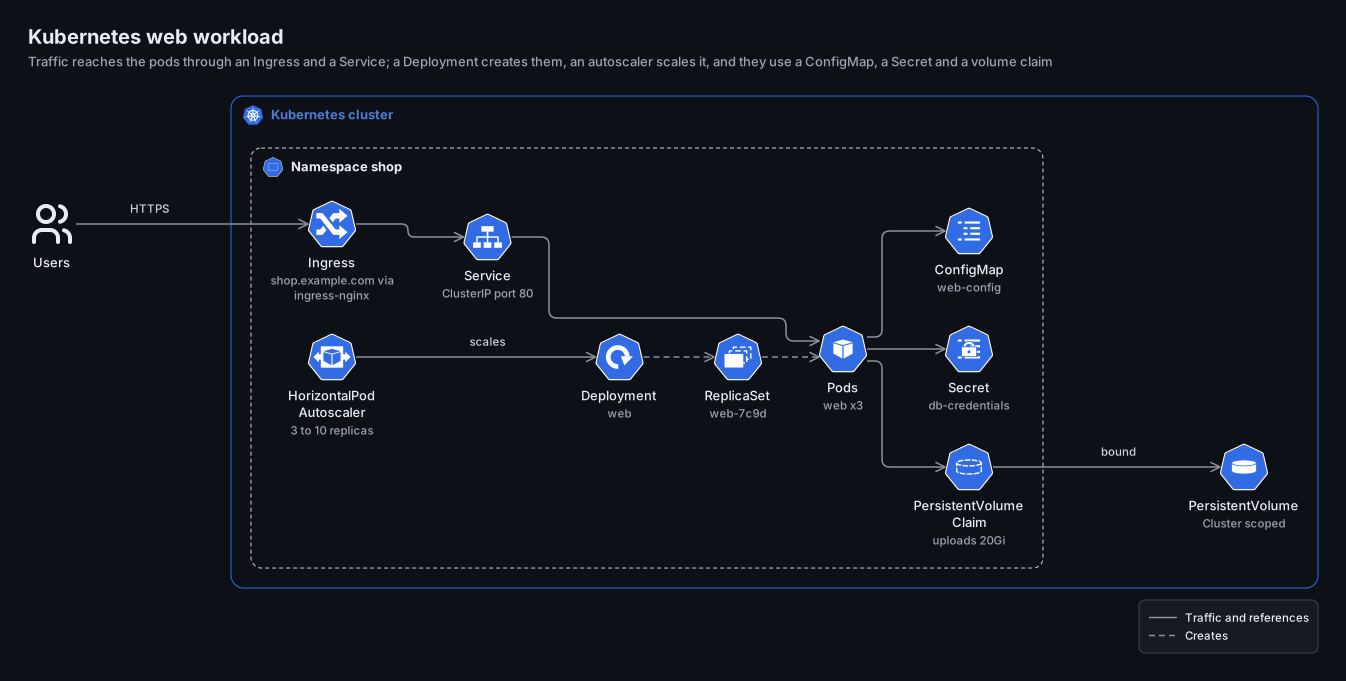
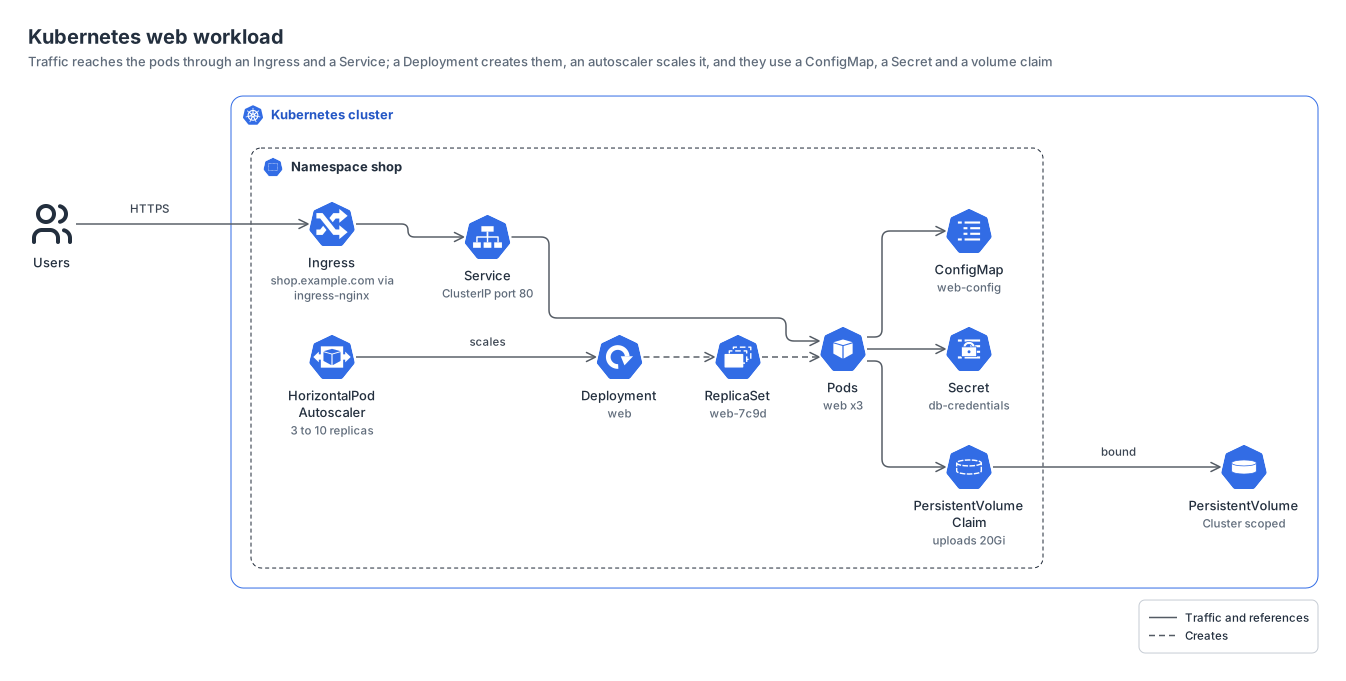
the official Kubernetes icons inside a namespace: Ingress, Service, Deployment, ReplicaSet, Pods, HorizontalPodAutoscaler, ConfigMap, Secret and a PersistentVolumeClaim bound to a PersistentVolume.
k8s11 nodes2 groups6 edges
k8s-workload.yamlOn GitHub
# yaml-language-server: $schema=../references/diagram.schema.json
title: Kubernetes web workload
subtitle: Traffic reaches the pods through an Ingress and a Service; a Deployment creates them, an autoscaler scales it, and they use a ConfigMap, a Secret and a volume claim
direction: right
layout: { merge: false, spacing: compact }

legend:
  solid: Traffic and references
  dashed: Creates

groups:
  cluster: { type: k8s:cluster, label: Kubernetes cluster }
  ns: { type: k8s:namespace, label: Namespace shop, in: cluster }

nodes:
  users: { icon: generic:users, label: Users }
  ing: { icon: k8s:ing, label: Ingress, note: shop.example.com via ingress-nginx, in: ns }
  svc: { icon: k8s:svc, label: Service, note: ClusterIP port 80, in: ns }
  hpa: { icon: k8s:horizontalpodautoscaler, label: HorizontalPodAutoscaler, note: 3 to 10 replicas, in: ns }
  deploy: { icon: k8s:deploy, label: Deployment, note: web, in: ns }
  rs: { icon: k8s:rs, label: ReplicaSet, note: web-7c9d, in: ns }
  pods: { icon: k8s:pod, label: Pods, note: web x3, in: ns }
  config: { icon: k8s:cm, label: ConfigMap, note: web-config, in: ns }
  secret: { icon: k8s:secret, label: Secret, note: db-credentials, in: ns }
  pvc: { icon: k8s:persistentvolumeclaim, label: PersistentVolumeClaim, note: uploads 20Gi, in: ns }
  pv: { icon: k8s:persistentvolume, label: PersistentVolume, note: Cluster scoped, in: cluster }

edges:
  # Traffic and references are solid; "creates" links are dashed, as in the Kubernetes deck.
  - users -> ing: HTTPS
  - ing -> svc -> pods
  - hpa -> deploy: scales
  - deploy --> rs --> pods
  - pods -> config, secret, pvc
  - pvc -> pv: bound
Start from this one
Copies the spec to diagram.yaml, then renders every format.
$ orrery init k8s-workload$ orrery render diagram.yaml -f all --theme both